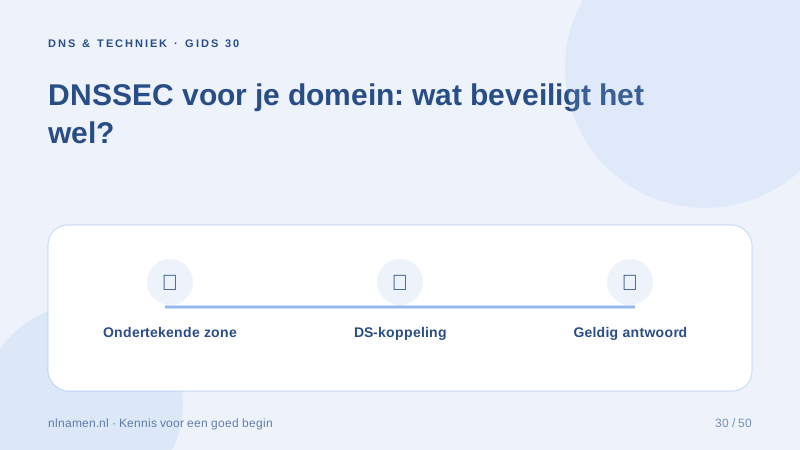
DNSSEC validates signed DNS information through a chain of trust. It does not replace HTTPS, mailbox security or account protection.
Keep the trust chain consistent
The parent’s DS information must match the DNS provider’s signing keys. A mismatch can make validating resolvers reject otherwise present DNS data.
Coordinate DNS-provider moves
New providers may use different signing keys. Changing nameserver names alone does not migrate DNSSEC. Coordinate the procedure and diagnose the mismatch before making security changes.
Check support and management separately
Extension support does not guarantee every panel exposes key management. Our current account focuses on nameservers and standard records; DNSSEC activation and key migration need a verified provider procedure.
Your practical checklist
- Verify actual DNSSEC status.
- Keep DS and DNSKEY consistent.
- Plan key handling during moves.
- Distinguish DNSSEC from HTTPS.
An old DS reference with a newly signed zone can break validation even when A and MX values look correct.
Sources and further reading
Registration rules and provider functions can change. Check the current requirements for your domain before ordering or changing services.
Ready for your own .nl?
€9.99 for year one, €12.99 renewal or 3 years for €27. No hosting required.
Check your domain →