DMARC evaluates authentication and visible-sender alignment, with a published policy for failures. Prepare carefully before enforcement.
Map legitimate mail streams
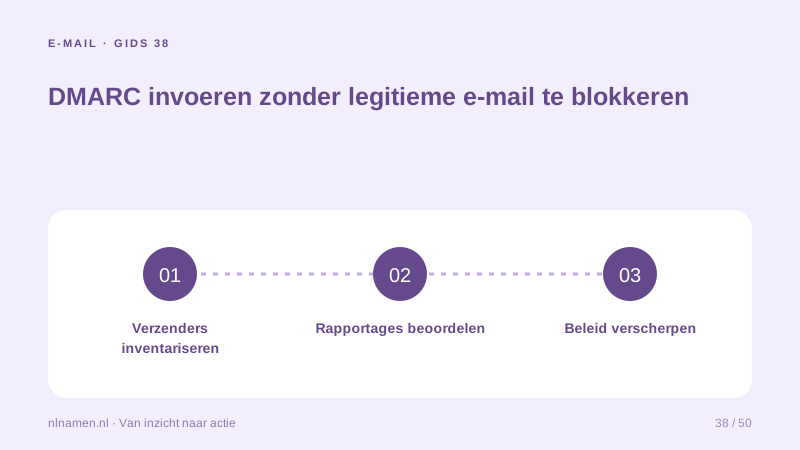
Inventory every sender and test its SPF and DKIM domains. Passing authentication alone is insufficient without the required alignment to the visible From domain.
Observe before enforcing
Monitoring can reveal missing legitimate senders before rejection. Use a reporting destination you control and actually analyse the reports before tightening policy.
Change one thing at a time
Preserve the previous record and coordinate changes with mail administrators. Retest forms and external senders after enforcement changes. DMARC is not a complete defence against all phishing.
Your practical checklist
- Inventory all senders.
- Verify SPF or DKIM alignment.
- Review reports before enforcement.
- Retest after every change.
A strict policy may affect invoices sent through an untested external system even when ordinary mailbox mail is configured correctly.
Sources and further reading
Registration rules and provider functions can change. Check the current requirements for your domain before ordering or changing services.
Ready for your own .nl?
€9.99 for year one, €12.99 renewal or 3 years for €27. No hosting required.
Check your domain →